Vulnerabilities
Reported on Arth’s public Bugcrowd researcher profile.
Independent security researcher
I’m Arth Bajpai, founder of AB Labs. I perform evidence-led security testing across web applications, APIs, Android, iOS, desktop applications, and network environments.
Track record
Hall of Fame recognition from Microsoft and Apple, alongside a public Bugcrowd record spanning 193 security programs.
Reported on Arth’s public Bugcrowd researcher profile.
Including 162 private Bugcrowd programs.
Selected from Arth’s acknowledgements and the top engagements shown on his downloaded public Bugcrowd profile.
View public Bugcrowd profile ↗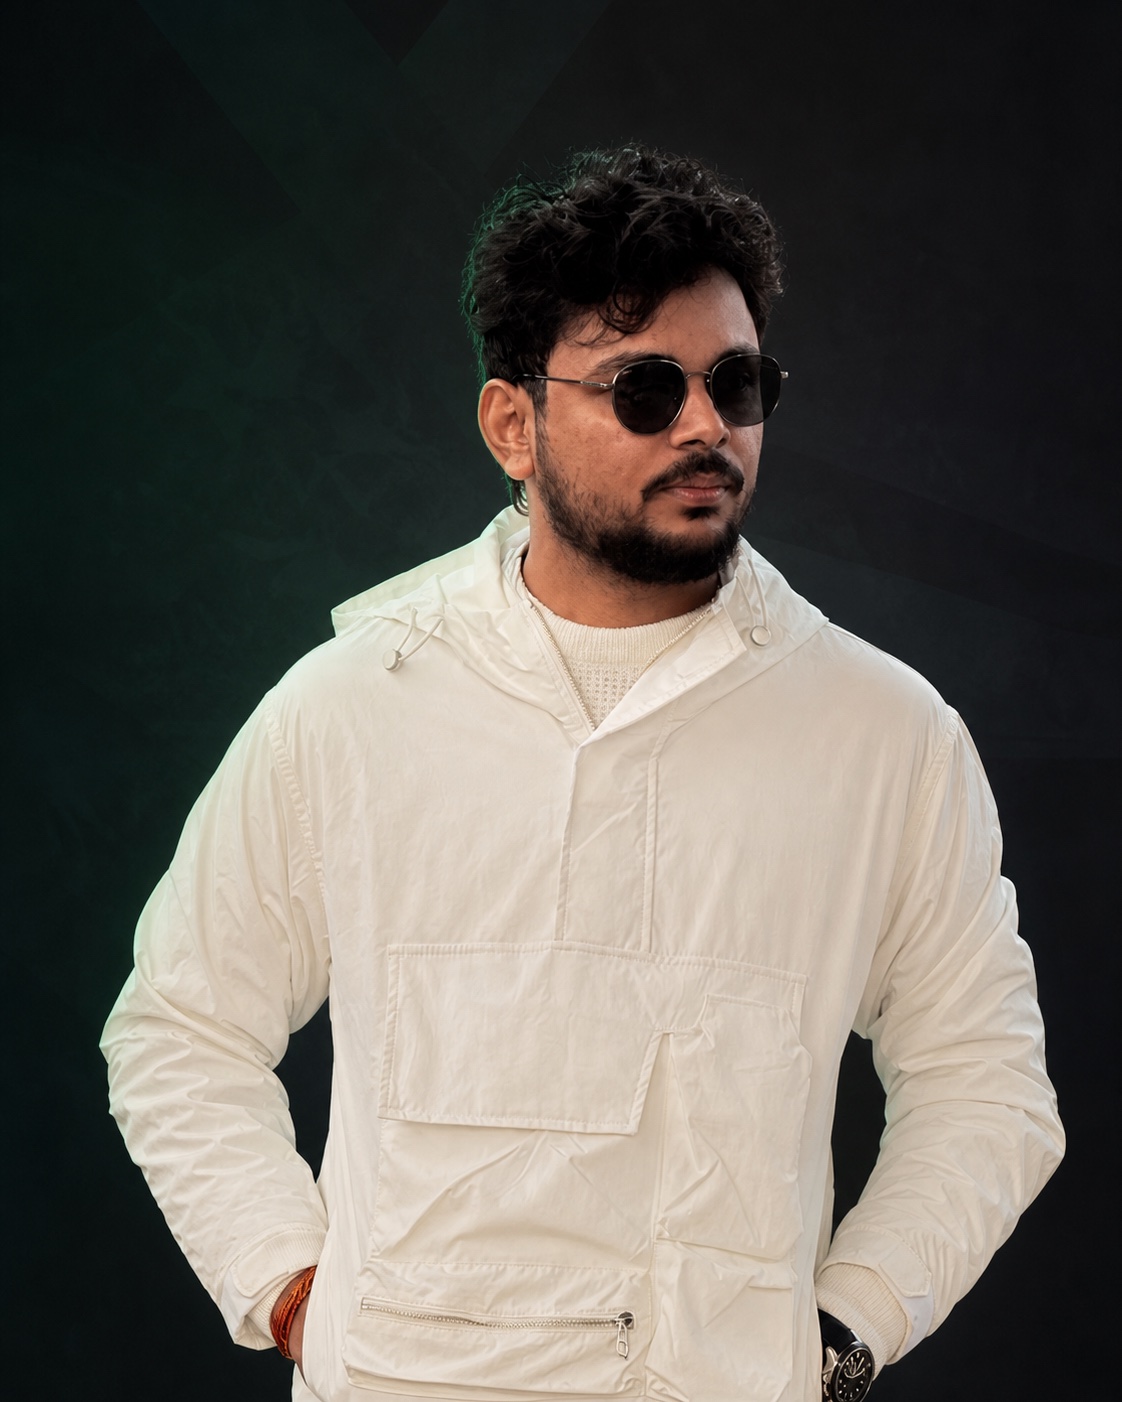
About Arth
I’m an India-based security researcher and the founder of AB Labs, focused on finding high-impact weaknesses across applications, APIs, mobile platforms, desktop software, and networks.
My work centers on authorization, authentication, business logic, and server-side trust boundaries—tested with minimum harm and documented with evidence engineering teams can reproduce.
Core expertise
Focused reviews built around real product behavior—not scanner volume or generic checklists.
Object, role, and tenant boundaries across APIs and complex workflows.
Account lifecycle testing from sign-in and recovery to session integrity.
Input that crosses parsers, renderers, integrations, and internal fetch boundaries.
Function-first assessment of modern API contracts and resolver authorization.
Security assessment across Android, iOS, desktop applications, network services, and the APIs and trust boundaries connecting them.
Engagements
End-to-end review of application flows, REST and GraphQL APIs, roles, tenants, and high-impact server-side attack paths.
Assessment of mobile application behavior, local storage, transport, platform controls, and supporting backend APIs.
Focused review of desktop applications, exposed services, network boundaries, configuration, and reachable attack paths.
A focused examination of authentication, authorization, GraphQL, integrations, or another critical boundary.
Independent confirmation that a fix closes the demonstrated path without leaving adjacent bypasses behind.
The AB Labs approach
The strongest findings usually live inside the application’s intended behavior: who owns an object, which role may perform an action, where input crosses a trust boundary, and what happens next.
Every engagement is designed around safe validation, precise evidence, and a report that engineering teams can reproduce quickly.
Start a conversation
Available for authorized web, API, Android, iOS, desktop, and network security testing, focused reviews, and remediation verification.
cybersecurity@arthbajpai.com